Blogs & Podcasts
Preparing for an AI + Post-Quantum World: Takeaways from the Forbes CIO Summit
Back to Blogs & Podcasts
19 Nov 2026
European security leaders face a hard question when they buy cybersecurity products: how do you prove a product meets EU standards instead of taking a vendor’s word for it? The EU’s answer is EUCC, the European Union Cybersecurity Certification scheme on Common Criteria. EUCC gives buyers an independent evaluation of a product against recognized EU requirements.
For CISOs planning a quantum-safe migration, EUCC adds a second test to vendor selection. Asking whether a post-quantum cryptography (PQC) product works is no longer enough. Regulated buyers in Europe now ask whether an independent body has evaluated it.
On November 10, 2026, Phio TX® version 4.5.6 became the first post-quantum cryptographic management platform awarded EUCC certification.
EUCC is the first cybersecurity certification scheme adopted under the EU Cybersecurity Act. It builds on Common Criteria (ISO/IEC 15408), the international standard for evaluating the security properties of IT products. ENISA, the EU Agency for Cybersecurity, maintains the scheme. Accredited labs across member states run the evaluations, and national certification bodies issue the certificates.
The point of EUCC is consistency. Before EUCC, a product certified in one EU country did not automatically carry weight in another. EUCC replaces the patchwork with one EU-wide mark. A product certified once is recognized across all 27 member states.
EUCC inherits the Common Criteria assurance scale, the Evaluation Assurance Levels (EAL1 through EAL7). A higher EAL means deeper testing, more design and code review, and stronger evidence requirements. EUCC groups these into two scheme levels, substantial and high, based on the rigor of the evaluation and the strength of the attacks a product must resist. EAL2, the level Phio TX was certified at, falls under substantial. It requires structured developer testing, design documentation, and independent vulnerability analysis by the evaluating lab, a recognized bar for commercial security products.
For US buyers, FIPS validation is the baseline. A FIPS certificate number is shorthand for one thing: an independent lab tested the product against a federal standard, and NIST issued proof. EUCC is becoming the European equivalent. Both frameworks give independent, government-recognized evidence that a product does what it claims, each in its own jurisdiction.
Three forces push EUCC from nice-to-have toward requirement:
The sectors feeling this first are: telecommunications providers, financial institutions, critical infrastructure operators, government agencies, and enterprises handling regulated data.
Quantum computing raises the stakes. Adversaries already practice Harvest Now, Decrypt Later (HNDL), collecting encrypted data today to decrypt once a capable quantum computer exists. AI-assisted cryptanalysis adds pressure on the same timeline. Long-shelf-life data such as financial records, health data, and state secrets is exposed the moment it crosses the wire.
PQC standards address the math. FIPS 203 standardized ML-KEM, the algorithm enterprises now deploy. Algorithms alone do not make a product trustworthy, though. A buyer needs proof the implementation is sound, and certification provides it.
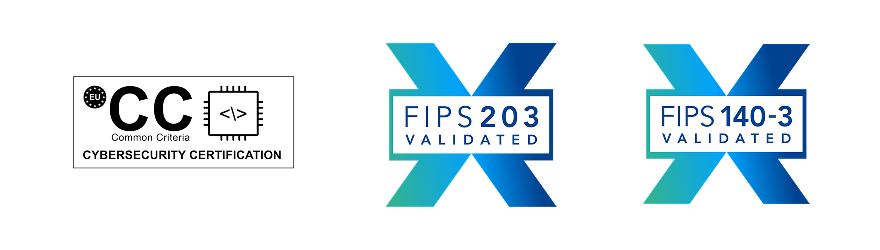
Phio TX®, the cryptographic management platform from Quantum XChange, secures data-in-motion by separating key generation and delivery from the data plane through a dual-path architecture. It strengthens existing encryption and supports PQC migration without rip-and-replace. Phio TX holds the industry’s first EUCC certification + FIPS 140-3 + FIPS 203 + Entropy validated stack:
Here is where the security industry earns its skepticism. Plenty of vendors list certifications they do not hold yet, sliding an “in process” cert into a datasheet as if a lab already signed off. CISOs have learned to read the footnotes.
Phio TX completed its Common Criteria (ISO/IEC 15408) evaluation at EAL2 and was awarded EUCC certification on November 10, 2026. Quantum XChange is now the only vendor to offer both FIPS validation and EUCC certification for a PQC solution. For multinational organizations, one platform now satisfies both US and European security assurance expectations, which means fewer parallel security reviews and one vendor-risk file instead of two.
“With Phio TX, Quantum XChange is the only vendor to offer both FIPS validation and EUCC certification for a post-quantum cryptography solution, giving organizations unmatched assurance as they prepare for the post-quantum era,” said Eddy Zervigon, CEO of Quantum XChange. “Customers need technologies that meet today’s compliance requirements while supporting long-term cryptographic resilience.”
Customers in regulated EU markets see the same need. “Operating in highly regulated markets means we need security solutions that are not only technically advanced, but also independently validated against recognized standards,” said Jacinto Cavestany, CEO at Evolutio. “Quantum XChange’s EUCC validation gives us greater confidence in Phio TX as we advance our quantum-safe strategy, support compliance obligations across EU jurisdictions, and protect the sovereignty of sensitive data across a highly distributed environment.”
EUCC also requires vendors to publish cybersecurity information for the certified product. For Phio TX, secure-use guidance, the security support period, and vulnerability reporting are available on the Phio TX cybersecurity information page.
The direction is set. For security leaders buying quantum-safe technology for European or global operations:
On the last point, Phio TX hot-swaps PQC algorithms with no downtime, no recertification cycle, and no maintenance window. When NIST or an EU body updates the algorithm set, the platform adapts in place. Algorithm agility is part of the architecture, not a roadmap promise.
EUCC is the European Union’s cybersecurity certification scheme, adopted under the EU Cybersecurity Act and based on Common Criteria (ISO/IEC 15408). It gives an independent, EU-wide evaluation of an IT product’s security properties. A product certified once is recognized across all member states, replacing the old country-by-country patchwork.
FIPS validation is the US standard, issued by NIST, proving a cryptographic product meets federal requirements. EUCC is the EU equivalent, based on Common Criteria and overseen by ENISA. Both give independent, government-recognized evidence of security. Enterprises operating across the US and Europe increasingly need both to satisfy regulators and procurement teams.
EUCC is voluntary today, but it is becoming a practical requirement. EU regulations including NIS2, DORA, and eIDAS 2.0 push regulated sectors toward demonstrable, independently evaluated security. Public-sector and critical-infrastructure tenders increasingly reference EUCC or Common Criteria, so vendors without certification risk being left off shortlists.
Yes. Phio TX version 4.5.6 is the first post-quantum cryptographic management platform awarded EUCC certification, certified at EAL2 under Common Criteria, certificate EUCC-3095-2026-000003-I-00. Phio TX also holds FIPS 140-3 (CMVP #4850), FIPS 203 (CAVP #6060), and Entropy (#E79) validations, making Quantum XChange the only vendor to offer both FIPS validation and EUCC certification for a PQC solution.
Post-quantum cryptography (PQC) replaces algorithms quantum computers will break. Standardized algorithms like ML-KEM address the math, but buyers still need proof the implementation is sound. EUCC and FIPS provide the independent evidence. For regulated European enterprises, pairing PQC with EUCC certification turns a security claim into an auditable fact.
A post-quantum migration is easier to defend to auditors and procurement teams when the platform carries issued certificates on both sides of the Atlantic. Phio TX holds FIPS validation and EUCC certification today.
Have one of our experts show you how Phio TX protects your organization from threats today and the quantum future.
Request Request
a a
demo demo